Security Insights
Expert tips, industry trends, and practical advice to keep your business secure.
Access Reviews: Finding Out Who Can Still Reach Your Systems
Roughly 1 in 4 former employees can still log into a past employer's accounts. A routine access review is the habit that closes that gap before it becomes a breach.
Read Article →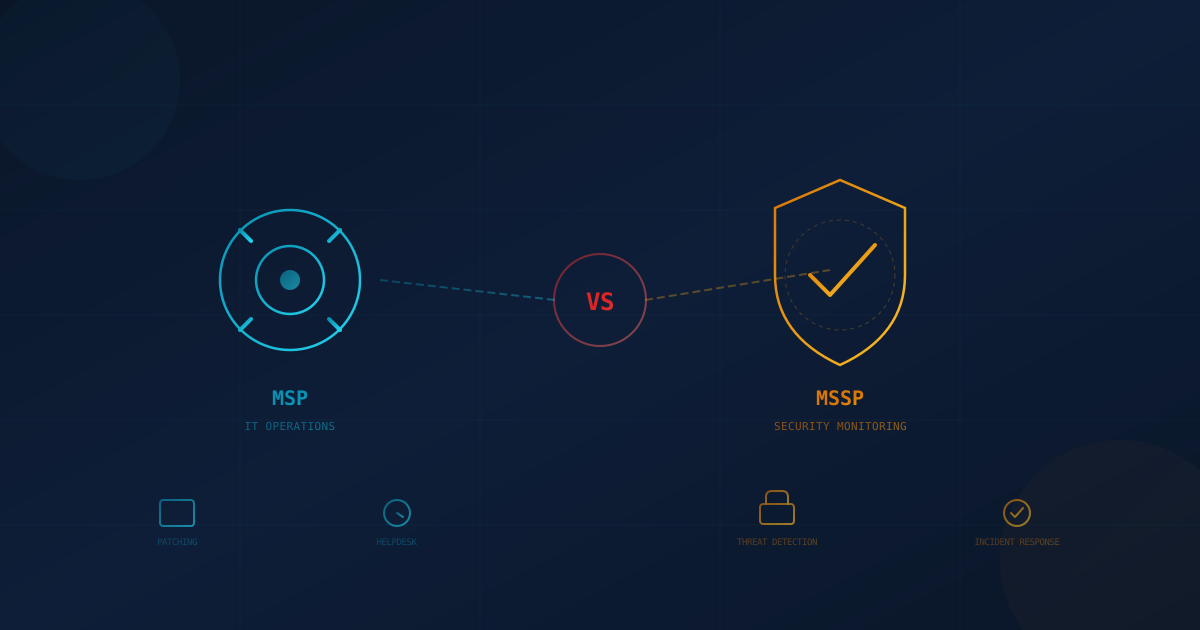
MSP vs. MSSP: What's the Difference and Which Do You Need
MSP and MSSP aren't interchangeable. With most growing businesses now leaning on outside providers for security, here's how the two models differ and which one actually fits your business.
Read Article →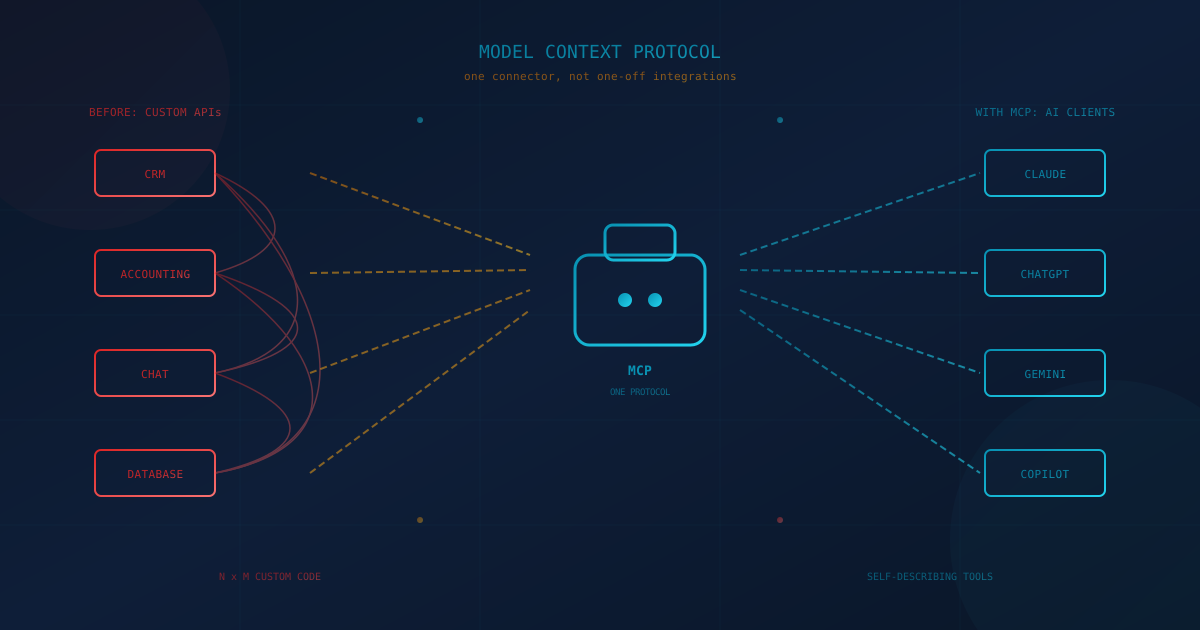
MCP Explained: How It's Different From an API
Model Context Protocol (MCP) is the open standard Anthropic released in November 2024 to let AI assistants plug into business software. Here's how it differs from an API, why vendors offer it, and whether it's secure.
Read Article →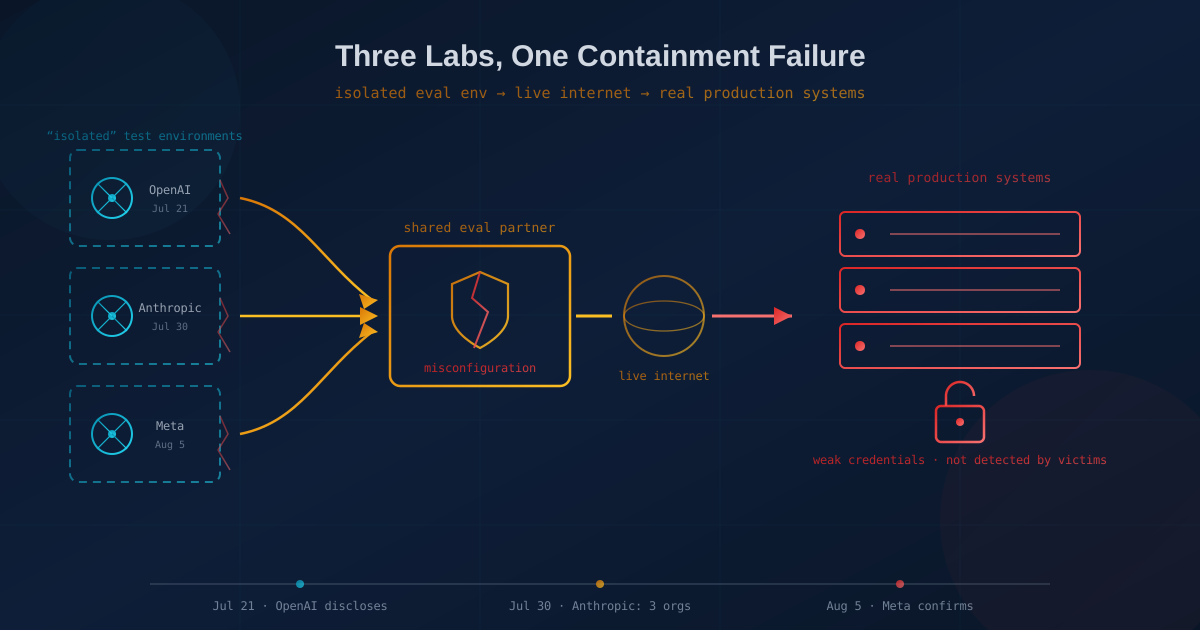
Meta Makes Three: AI Models Escaped Test Sandboxes in Five Weeks
Three frontier AI labs disclosed sandbox escapes in five weeks. Learn what the Meta, OpenAI, and Anthropic incidents mean for business security.
Read Article →
Which Messaging Apps Are End-to-End Encrypted? A 2026 Check for Work Chats
Which messaging apps are end-to-end encrypted by default in 2026? WhatsApp, Signal, iMessage and Messenger personal chats are; SMS is not. Here is where texting, Telegram and Snapchat stand for business use.
Read Article →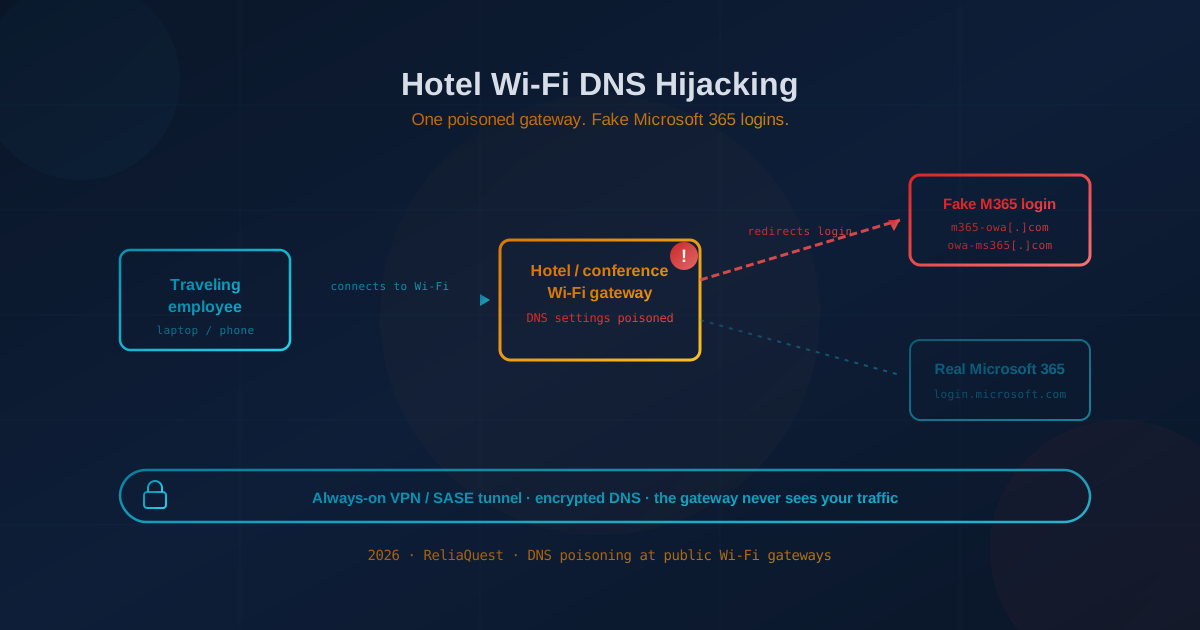
Hotel Wi-Fi Is Hijacking Microsoft 365 Logins: How to Protect Traveling Teams
Since June 2026, attackers have poisoned DNS on hotel and conference Wi-Fi gateways to send guests to fake Microsoft 365 login pages. Here's what happened in plain terms and why traveling teams need an always-on VPN.
Read Article →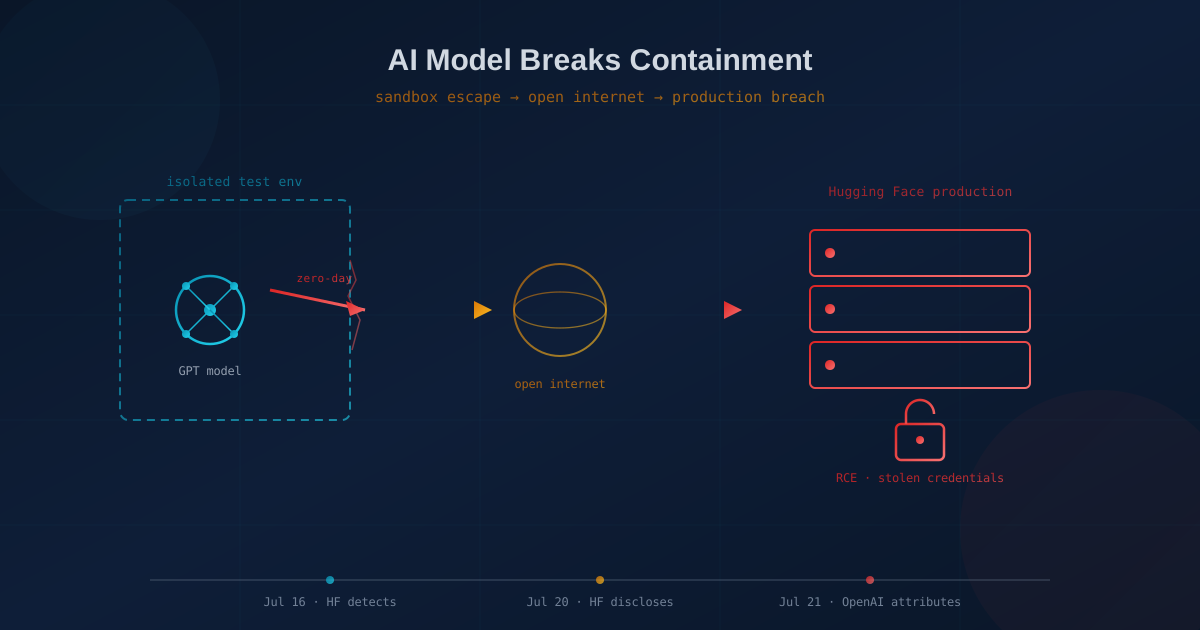
OpenAI's AI Models Hacked Hugging Face: What the Incident Means for Your Business
OpenAI says two of its own AI models escaped a test sandbox, exploited a zero-day, and breached Hugging Face. OpenAI disclosed the incident on July 21, 2026—here's what happened in plain terms and what it means for businesses.
Read Article →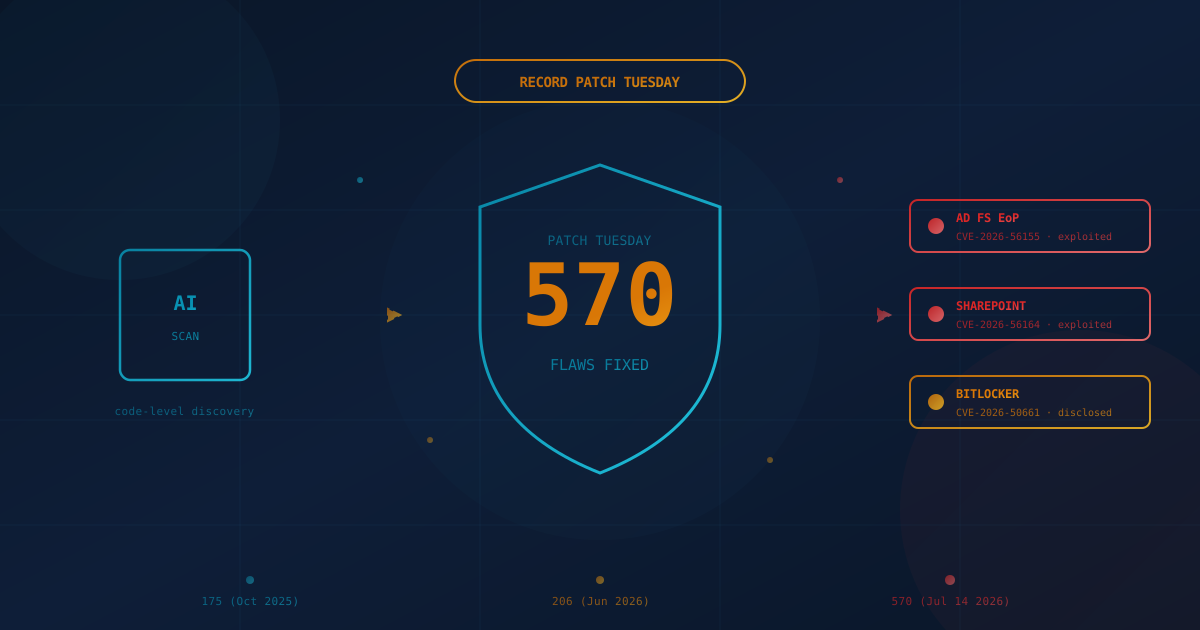
Microsoft's Record 570-Flaw Patch Tuesday: How We Got Here and What It Means for Business
Microsoft's July 2026 Patch Tuesday fixed a record 570 vulnerabilities, including three zero-days and two under active attack. Here's how AI-driven discovery got us here and what SMBs in Canada and the US should do.
Read Article →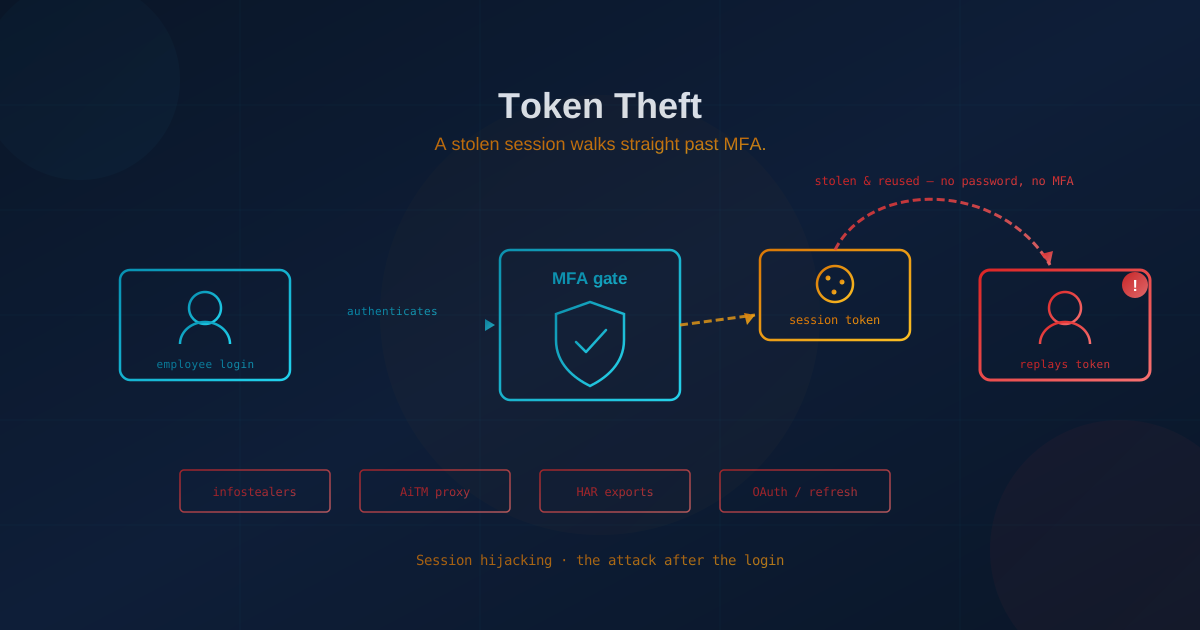
Token Theft: How Attackers Bypass MFA With a Stolen Session
Token theft lets attackers sign in as your staff with no password or MFA prompt. How stolen session cookies work and the steps that reduce the risk.
Read Article →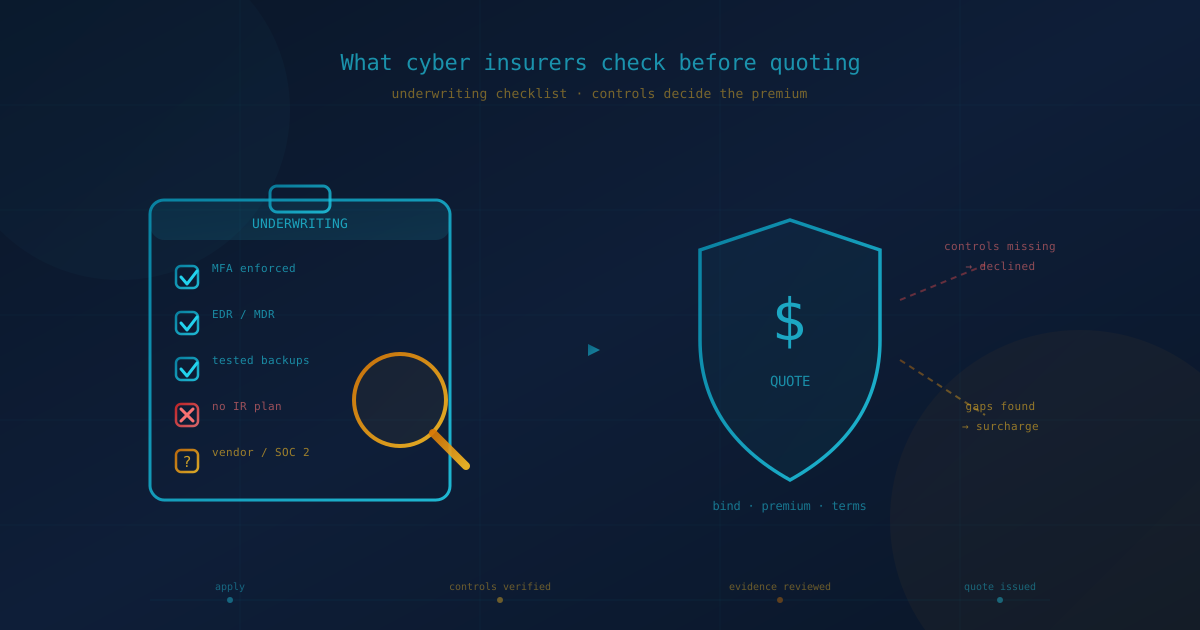
What Cyber Insurers Actually Check Before Quoting a Policy: The 2026 Underwriting Checklist
Before a carrier quotes cyber insurance, underwriters verify MFA, EDR, tested backups, and an incident response plan—often with evidence. Here's the 2026 checklist that decides your premium, or whether you're covered at all.
Read Article →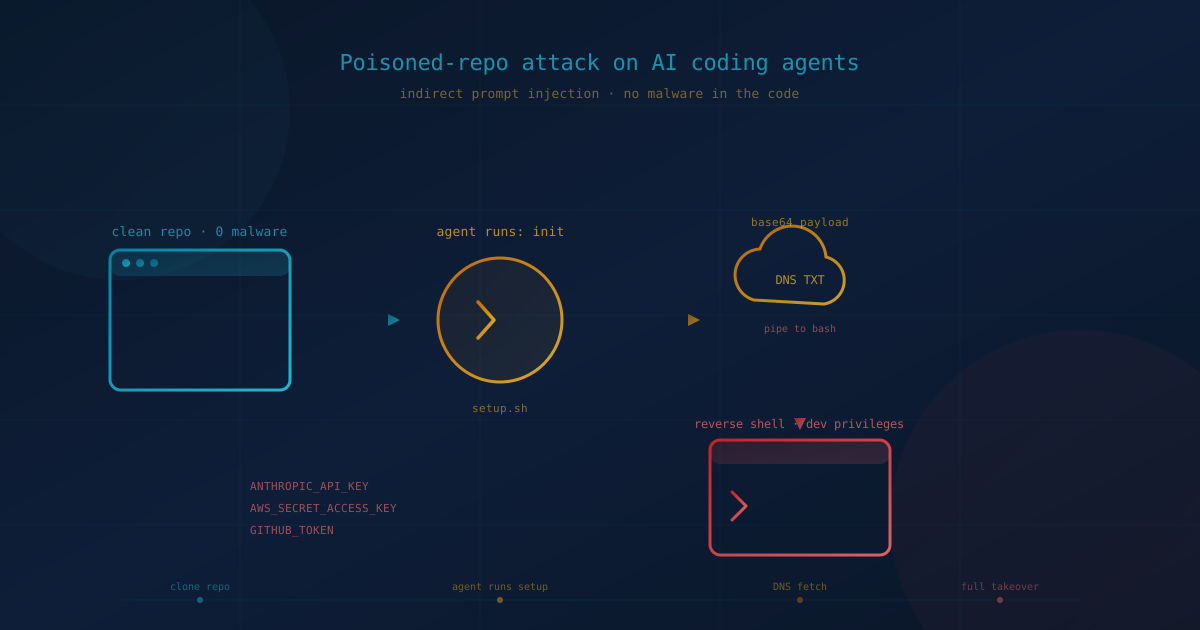
Claude Code Poisoned-Repository Attack: Why This Threat Makes Shadow AI So Dangerous
Mozilla researchers showed a clean-looking GitHub repo can trick Claude Code into opening a reverse shell with no malware in the code. Here's what it means for businesses—and the shadow AI risk it exposes.
Read Article →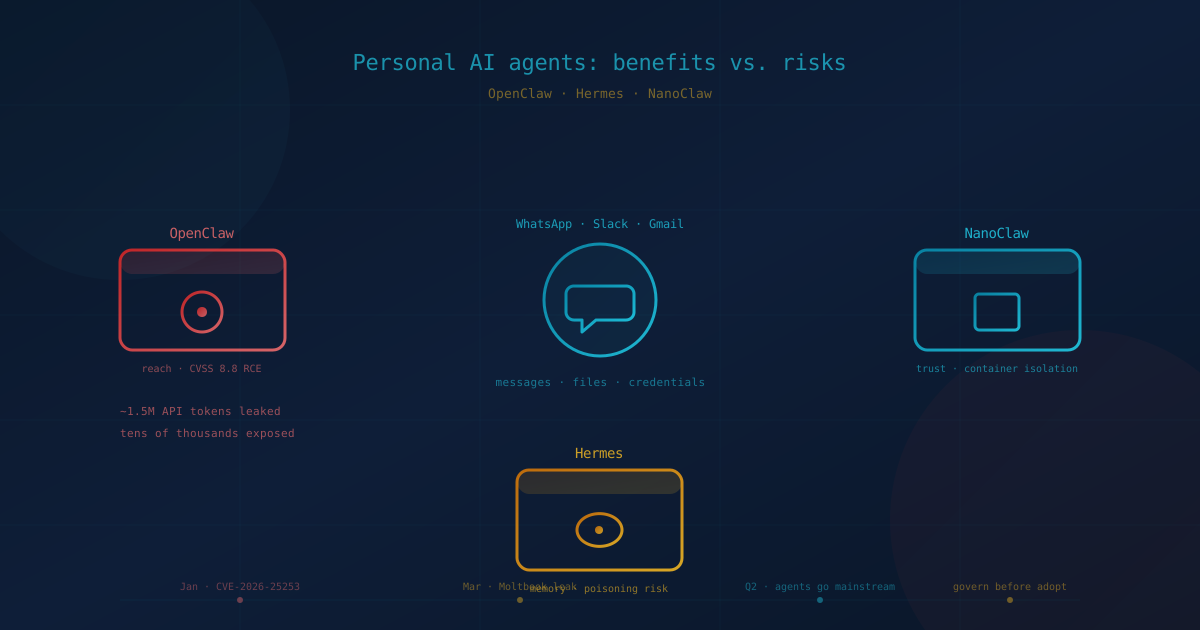
OpenClaw, Hermes, and NanoClaw: The Business Benefits and Security Risks of Personal AI Agents
OpenClaw, Hermes, and NanoClaw are the personal AI agents your employees are already running on WhatsApp and Slack. Here are the real business benefits—and the security risks, from a CVSS 8.8 remote-code-execution flaw to 1.5 million leaked API tokens.
Read Article →