Security Insights
Expert tips, industry trends, and practical advice to keep your business secure.
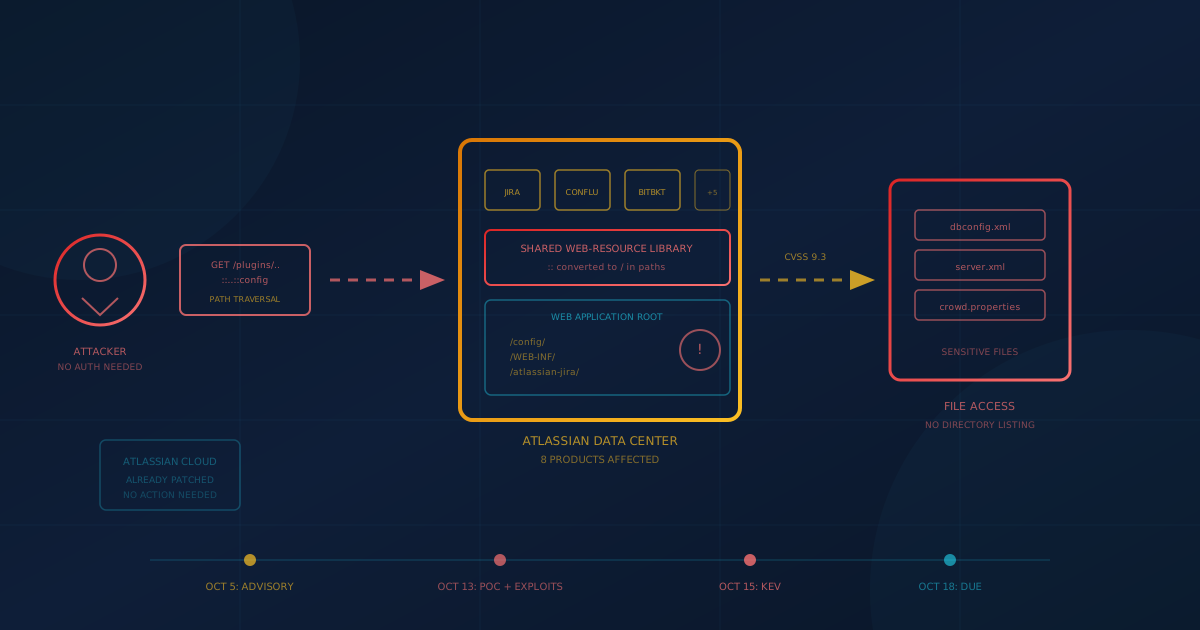
Atlassian Data Center Flaw CVE-2026-21589: Patch Jira and Confluence Now
CVE-2026-21589 is an actively exploited arbitrary file access vulnerability affecting Atlassian Jira, Confluence, Bitbucket, and five other Data Center products. CISA added it to the KEV catalog on October 15, 2026, with a federal remediation deadline of October 18.
Read Article →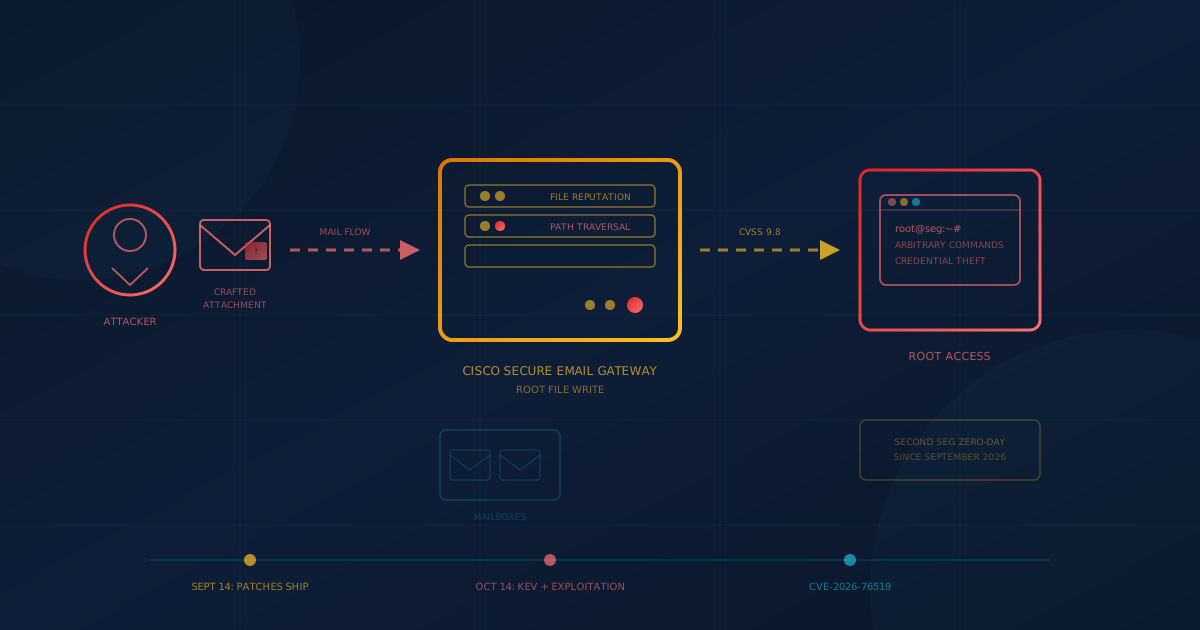
Cisco Secure Email Gateway Exploited: One Attachment Can Root the Appliance
CVE-2026-76519 is an actively exploited Cisco Secure Email Gateway vulnerability that lets attackers write files and execute commands as root by sending a crafted email attachment. CISA added it to the KEV catalog on October 14, 2026. Here is what SMBs need to know.
Read Article →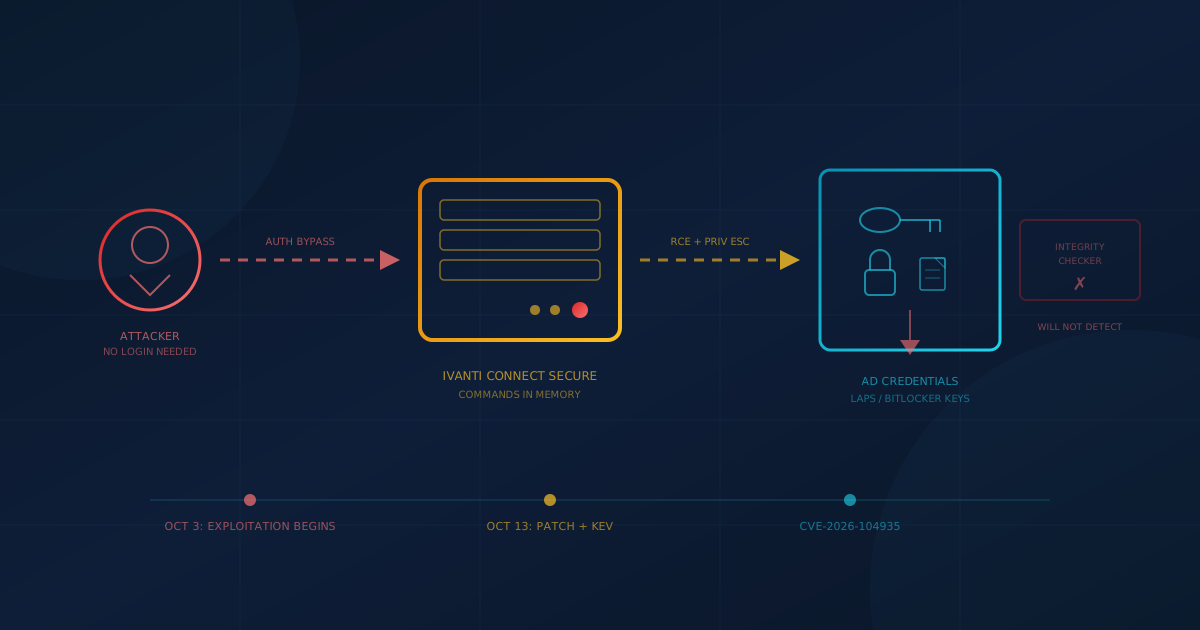
Ivanti Connect Secure Zero-Day: Patch CVE-2026-104935 Now
CVE-2026-104935 is an actively exploited Ivanti Connect Secure zero-day that bypasses authentication and allows remote command execution. CISA added it to the KEV catalog on October 13, 2026. Here is what SMBs using remote-access VPNs need to know.
Read Article →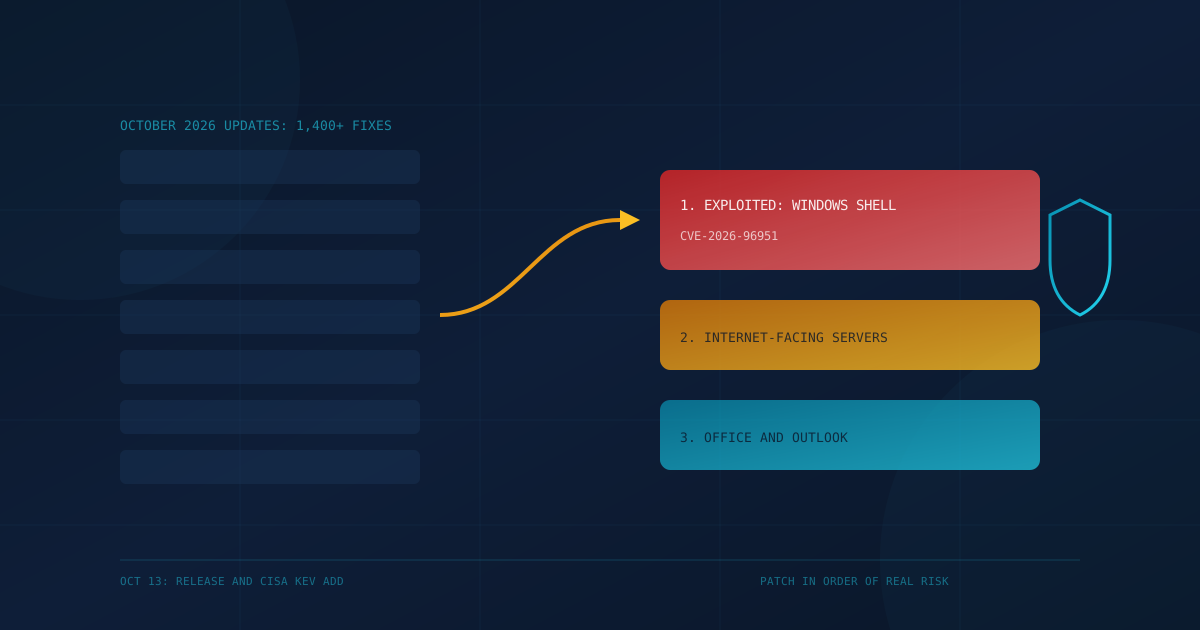
Microsoft October 2026 Patch Tuesday: What to Patch First This Week
Microsoft's October 2026 Patch Tuesday fixed more than 1,400 flaws, including a Windows Shell zero-day (CVE-2026-96951) already exploited in attacks. Here is the order small businesses should patch in.
Read Article →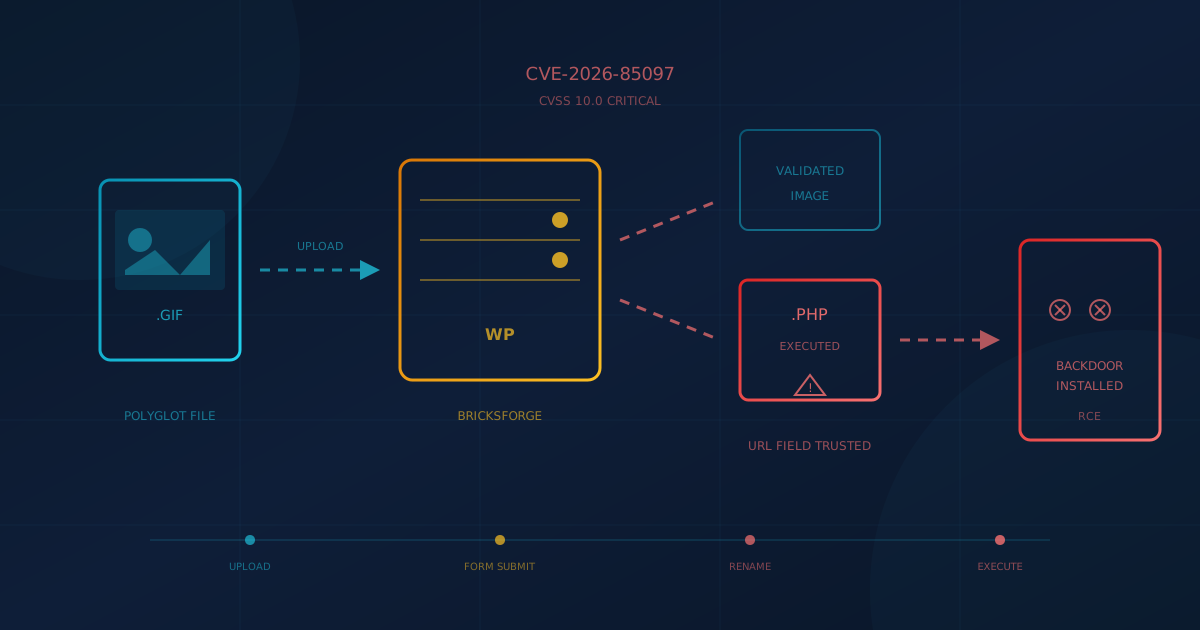
Bricksforge Vulnerability Exploited in the Wild: What WordPress Site Owners Need to Do
CVE-2026-85097, a critical Bricksforge vulnerability rated CVSS 10.0 by Patchstack, has been actively exploited since October 7, 2026. WordPress sites running affected versions should update immediately.
Read Article →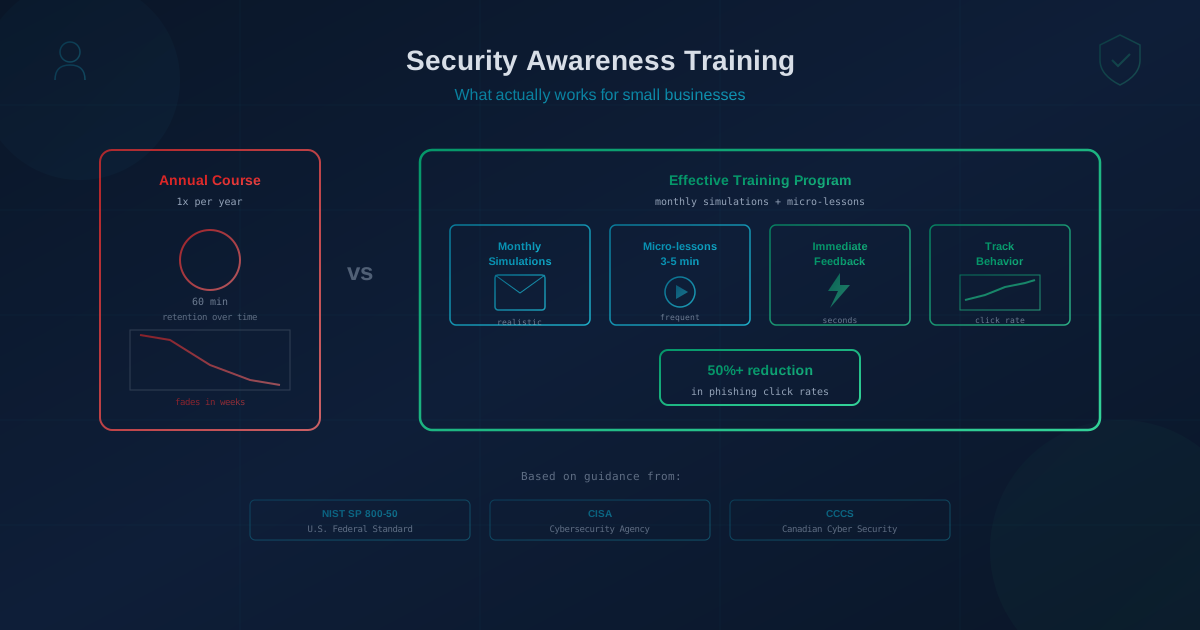
Security Awareness Training That Works for Small Businesses
CCCS, CISA, and NIST research shows that short, frequent simulations and just-in-time reminders reduce click rates more than long annual courses. Here is what actually changes employee behavior.
Read Article →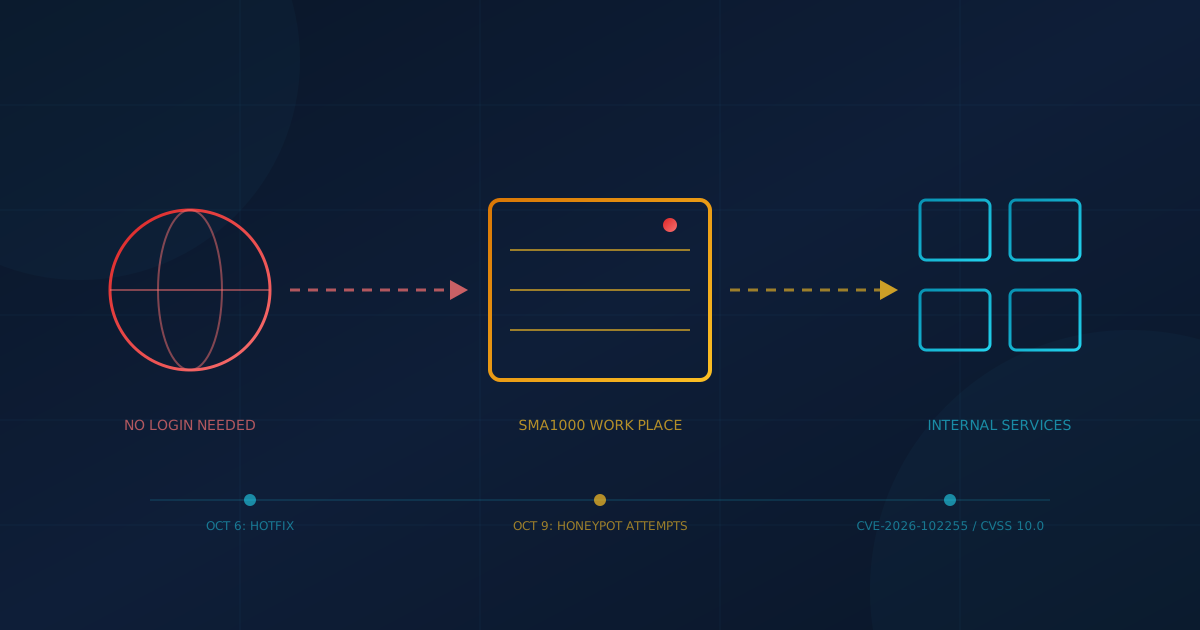
SonicWall SMA1000 Flaw Rated 10.0: Check Your Remote Access Gateway
The SonicWall SMA1000 flaw CVE-2026-102255 scores 10.0 and needs no login. It was patched October 6, 2026, and honeypots saw exploitation attempts by October 9. Here is what to check.
Read Article →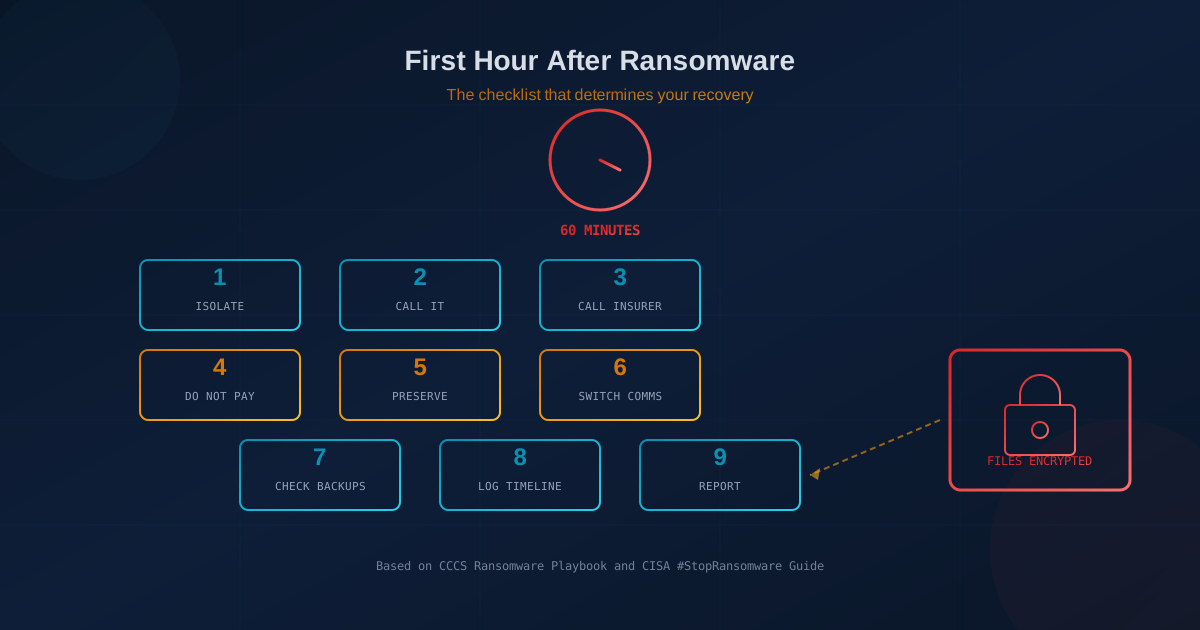
Ransomware Attack? What to Do in the First Hour
The first hour after a ransomware attack determines your recovery. Follow this step-by-step checklist: isolate devices, contact your IT provider and insurer, preserve evidence, and report to authorities.
Read Article →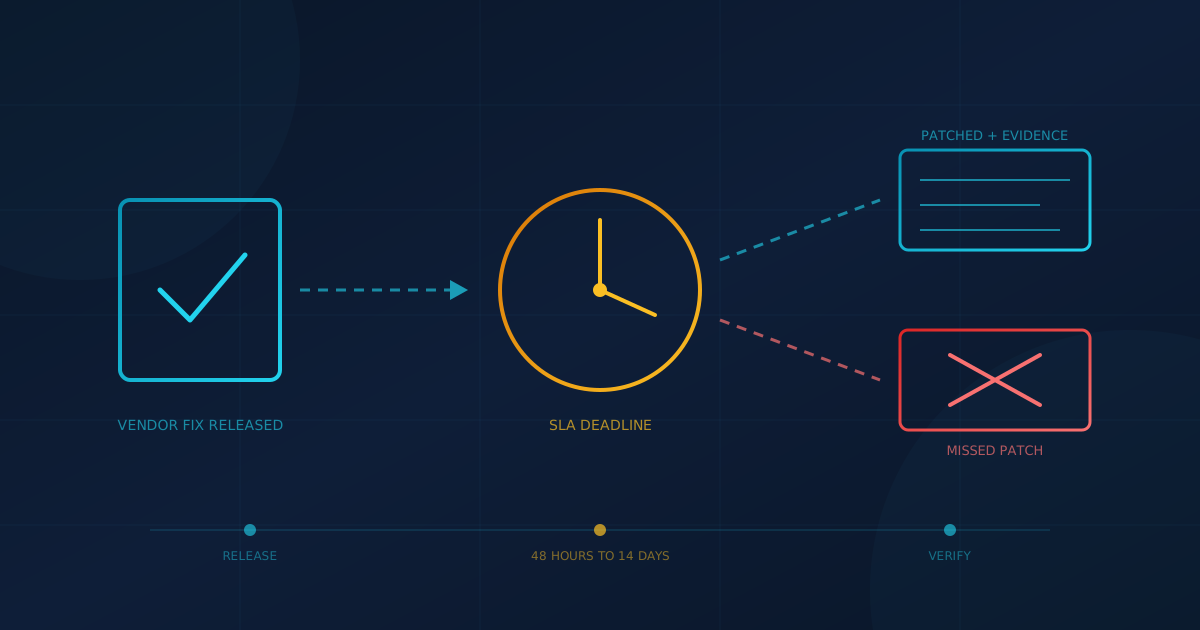
The FBI's Missed Patch: How to Set a Patch SLA With Your IT Provider
The FBI blamed its September 2026 breach on a contractor's missed security patch. A patch SLA puts deadlines and proof in writing. Here is what SMBs in the US and Canada should ask for.
Read Article →
Do You Need a Managed Firewall for a Small Office?
A managed firewall service handles firmware patching, rule reviews, VPN hardening, logging, and configuration backup so your IT provider keeps the perimeter secure. Here is when it makes sense.
Read Article →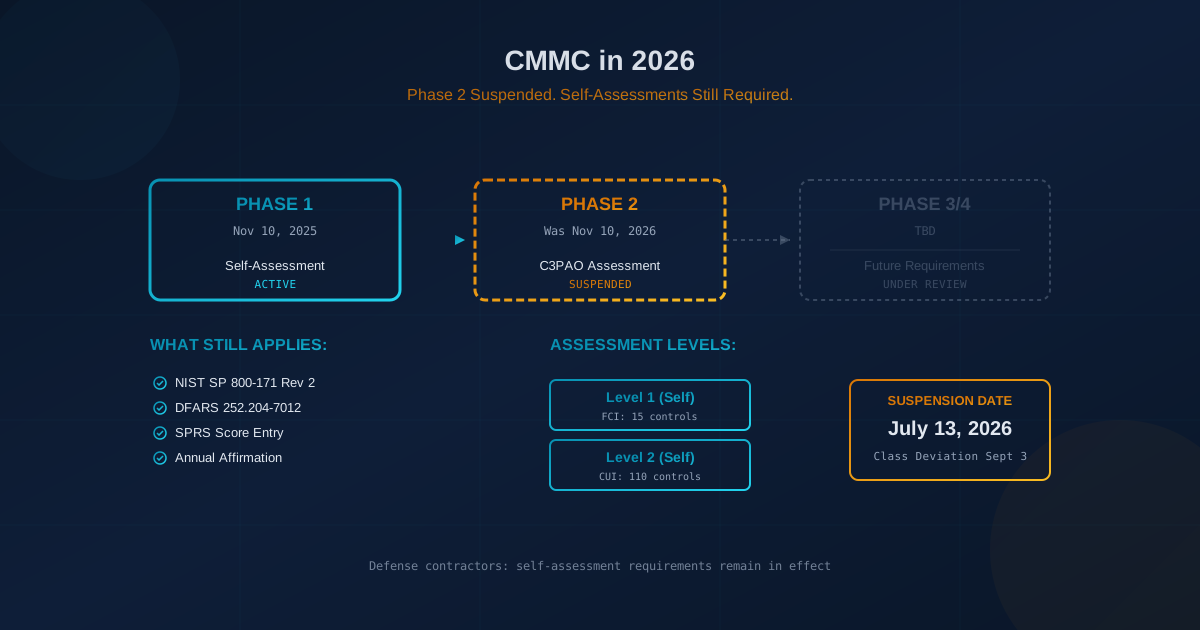
CMMC in 2026: Phase 2 Is Suspended. Does Your Small Business Still Need It?
CMMC Phase 2 was suspended on July 13, 2026. Phase 1 self-assessments, SPRS scores, and NIST SP 800-171 Rev 2 compliance still apply. Here is what small businesses working with US defense contractors need to know.
Read Article →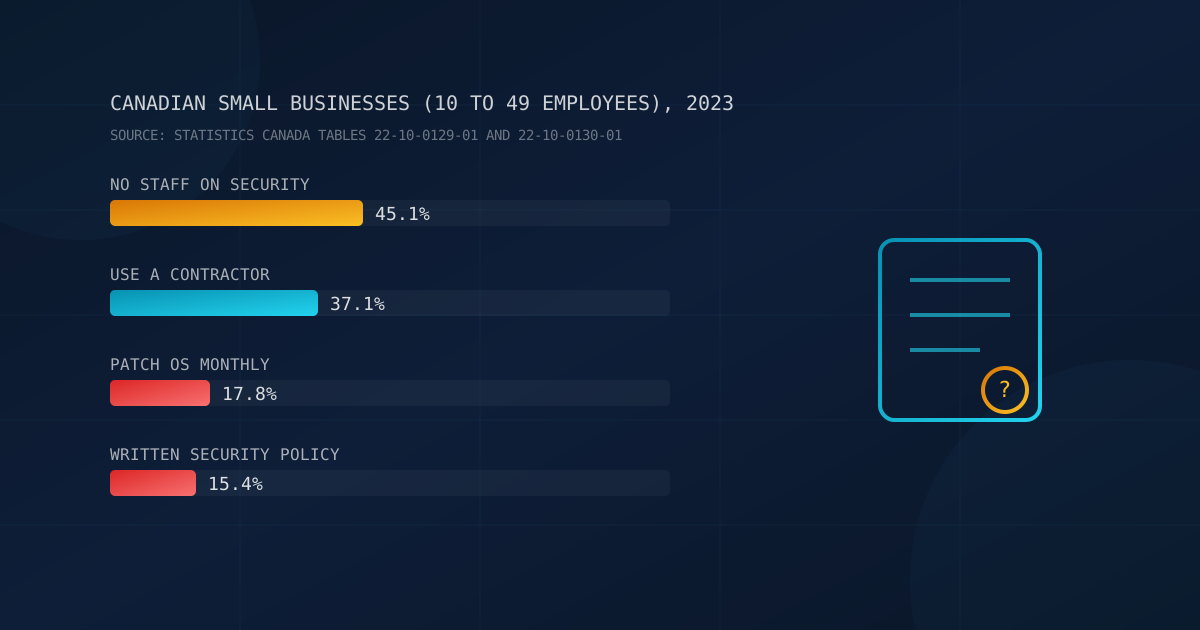
Canadian Small Business Cyber Risk Report 2026: 5 Questions for Your IT Provider
The Canadian Small Business Cyber Risk Report 2026 finds 45.1% of firms with 10 to 49 employees have no staff doing security tasks and 17.8% patch monthly. Five questions to put to your IT provider.
Read Article →