Security Insights
Expert tips, industry trends, and practical advice to keep your business secure.
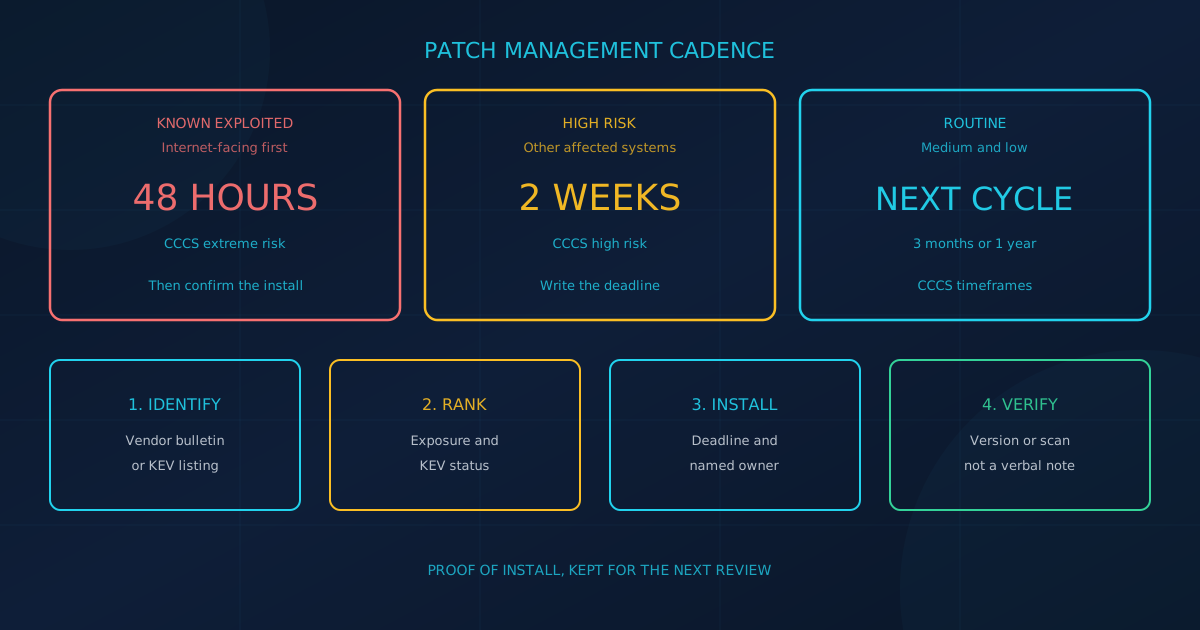
Patch Management for Small Businesses
Patch management for small businesses needs a written cadence. CISA revoked BOD 22-01 on June 10, 2026. CCCS still sets 48-hour extreme-risk guidance.
Read Article →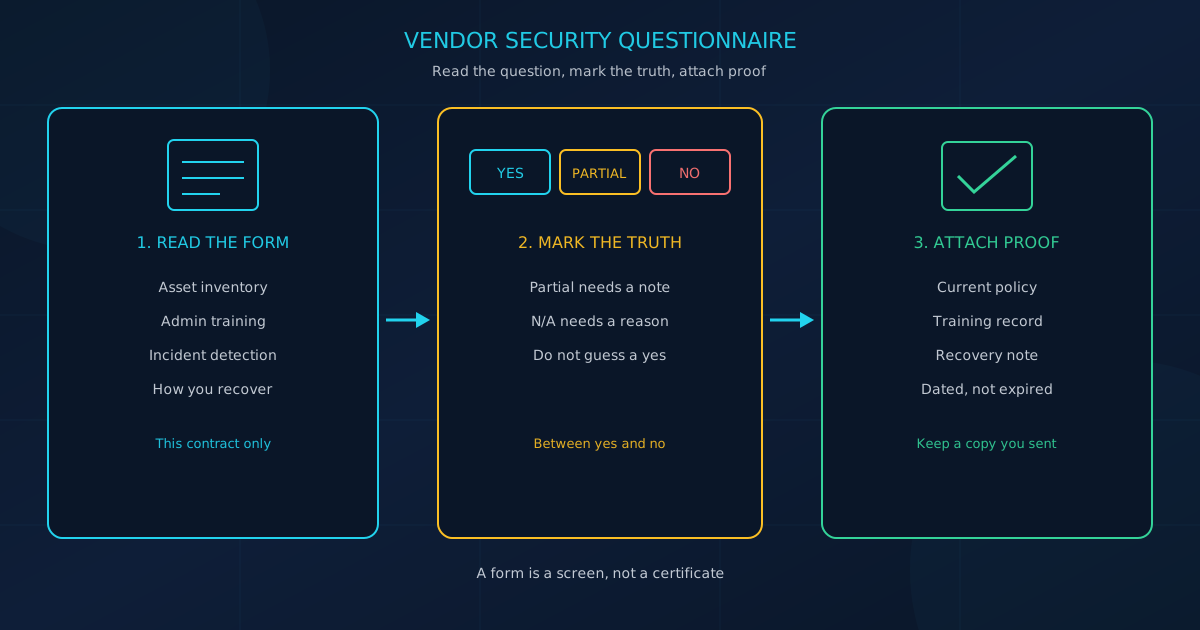
Vendor Security Questionnaires for SMBs
Vendor security questionnaires need evidence, not a blanket yes. CISA's April 2021 template says to attach supporting documents.
Read Article →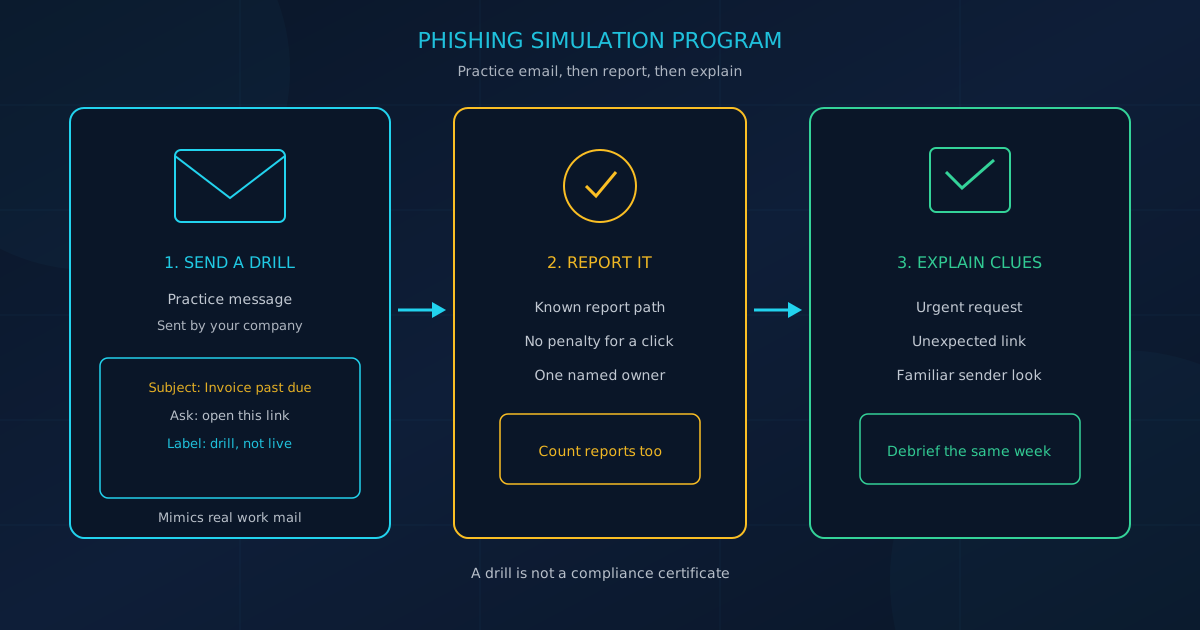
Phishing Simulations for Small Business
Phishing simulations for small business are practice emails you send your own staff. Here is how to run them without blame.
Read Article →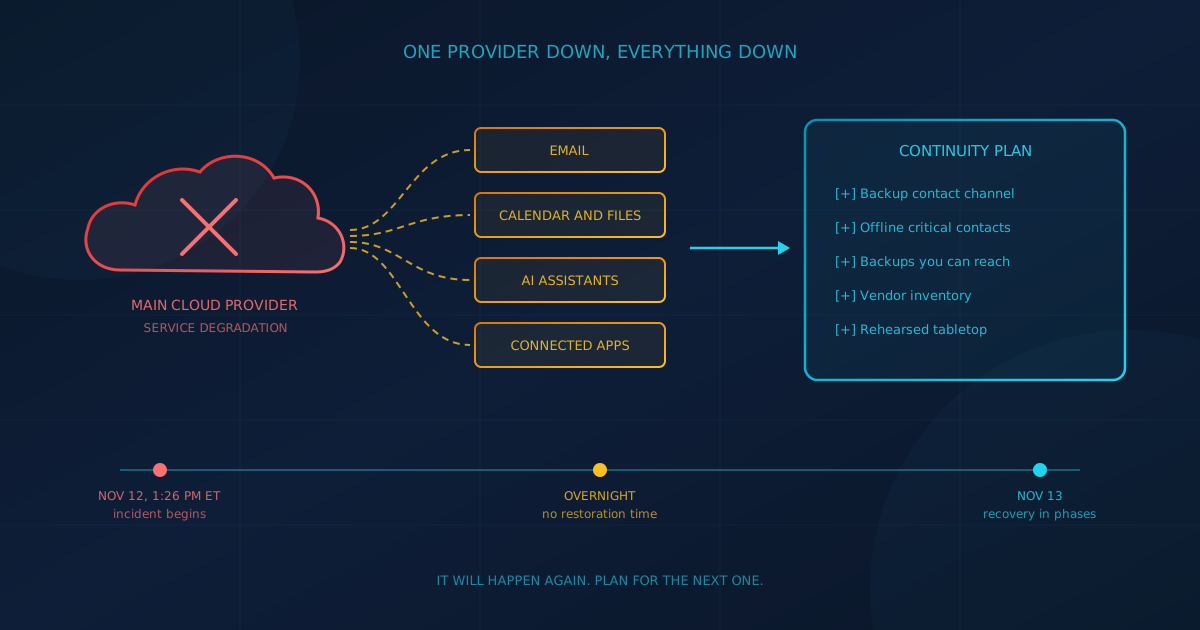
Microsoft 365 Outage: It Will Happen Again
The Microsoft 365 outage that began Nov 12, 2026 ran past 20 hours. Any cloud provider can fail this way. Here is how to keep working when one does.
Read Article →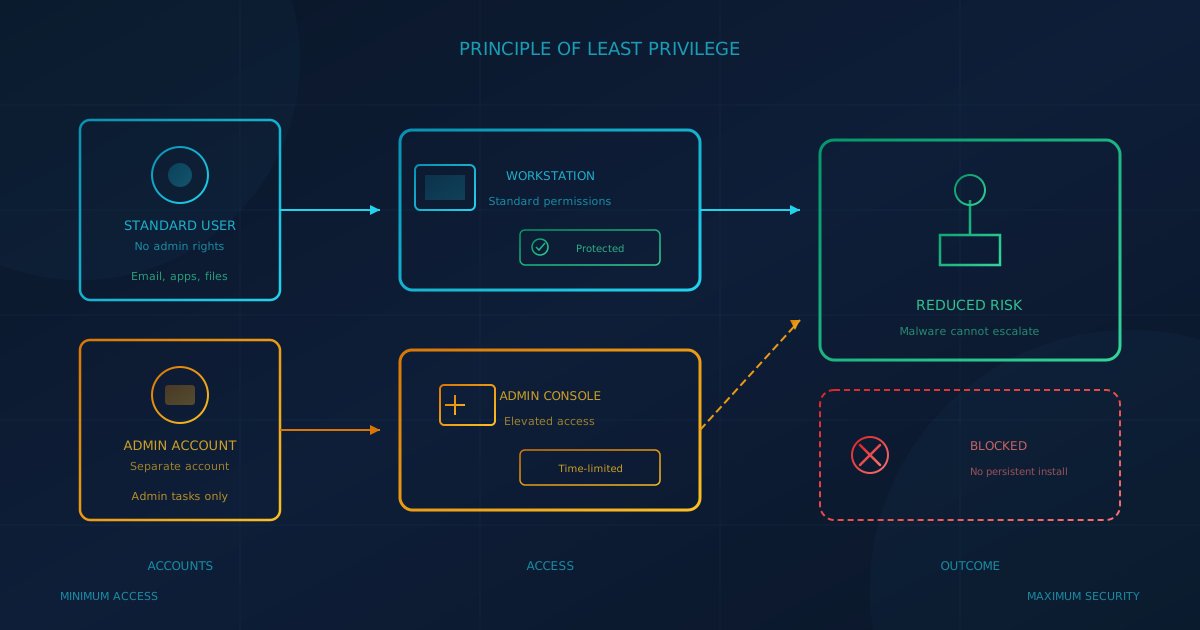
Least Privilege for Small Business
Least privilege for small business means removing local admin rights from everyday accounts. Here is why it matters and how SMBs can roll it out safely.
Read Article →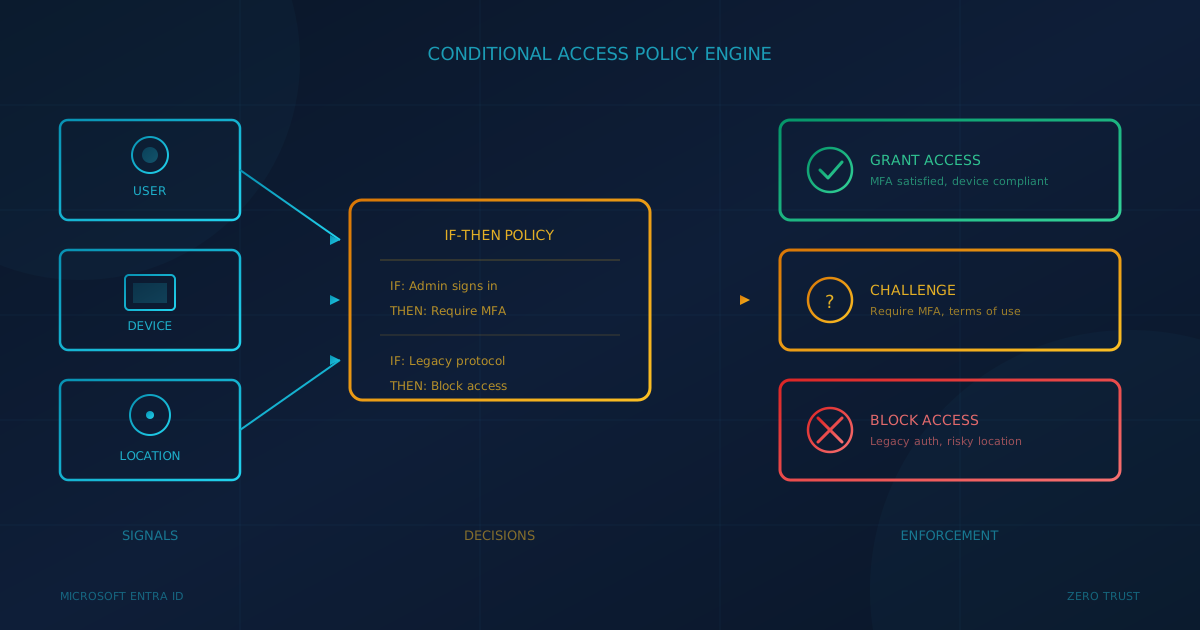
Conditional Access for Small Business
Conditional Access for small business requires MFA, blocks risky sign-ins, and enforces device rules. Here are the starter policies Microsoft recommends.
Read Article →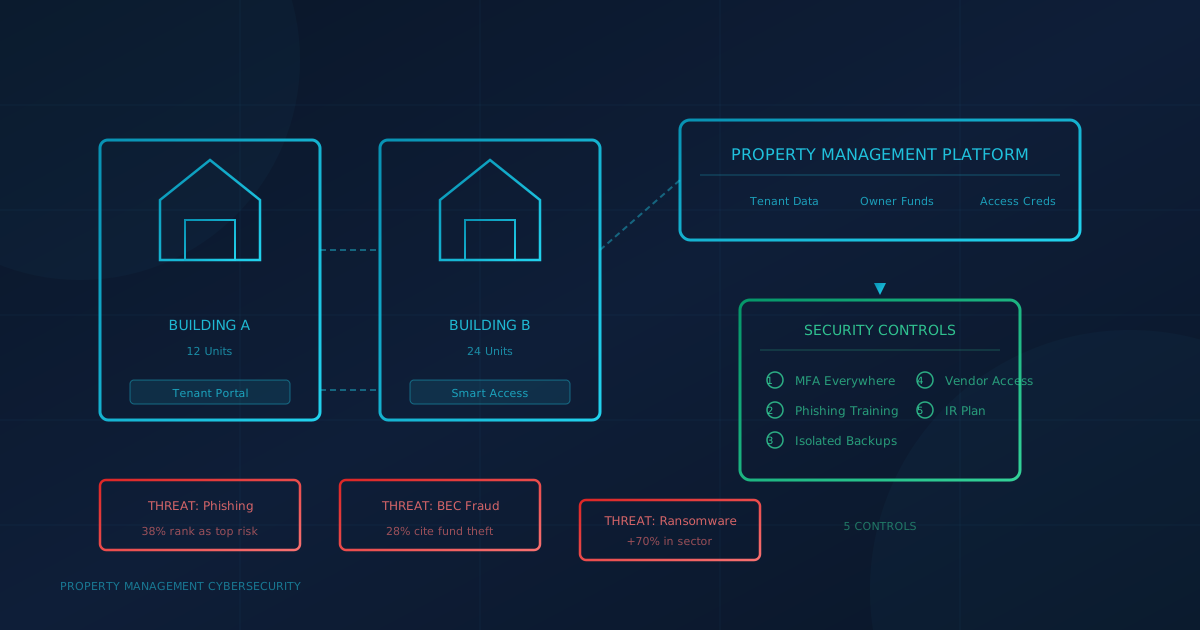
Cybersecurity for Property Management Companies
Property management firms hold tenant data, owner funds, and building system access. These five controls address the threats that hit the sector hardest.
Read Article →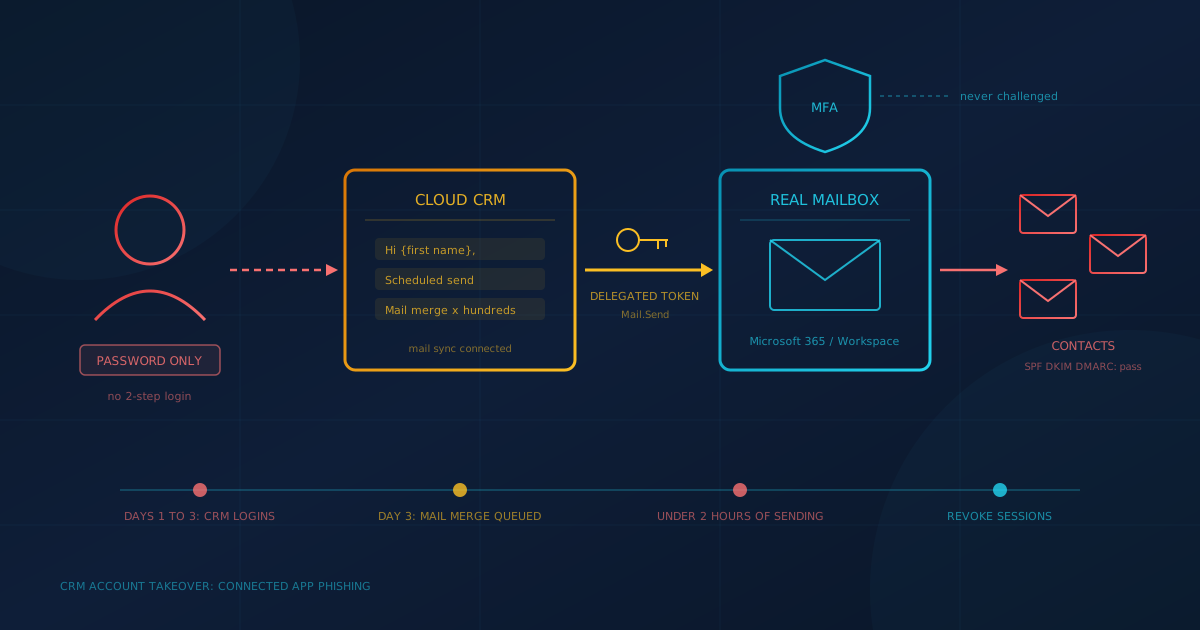
CRM Account Takeover: How a Phish Got Past MFA
A CRM account takeover let an attacker send phishing from a real Microsoft 365 mailbox without ever signing in to it. How connected apps sidestep MFA, and how to check yours.
Read Article →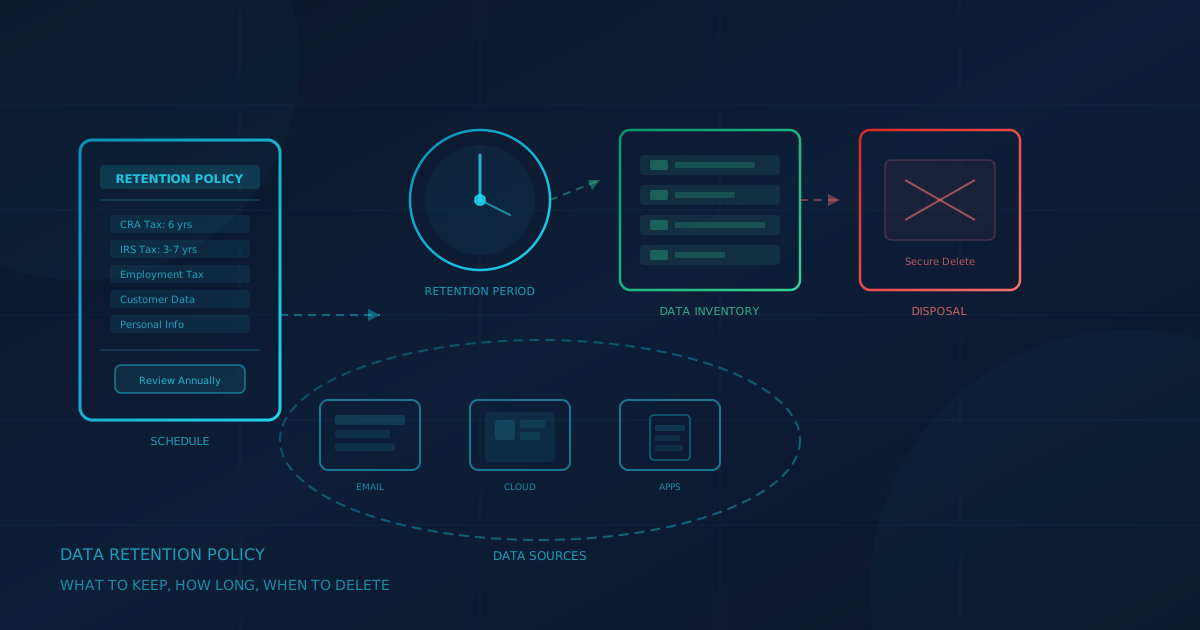
Data Retention Policy for Small Business
A data retention policy defines what data to keep, how long, and when to delete it. Here is how SMBs in Canada and the US can build one.
Read Article →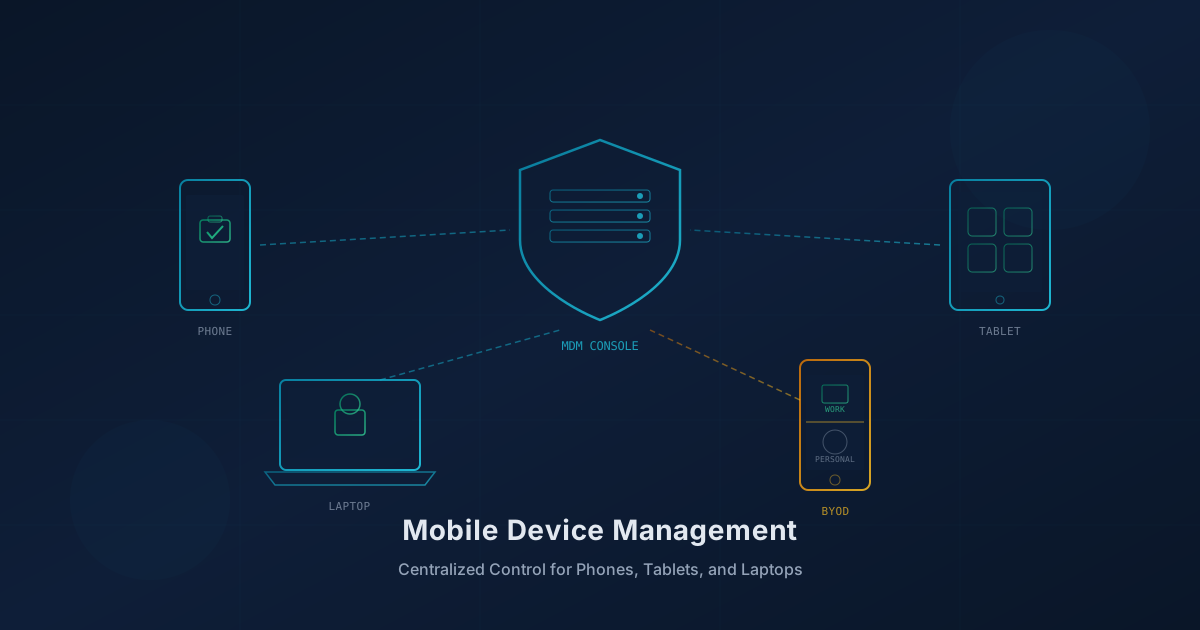
Mobile Device Management for Small Business
Mobile device management (MDM) lets a business enforce passcodes, push apps, and remotely wipe lost phones. Here is what MDM does and when you need it.
Read Article →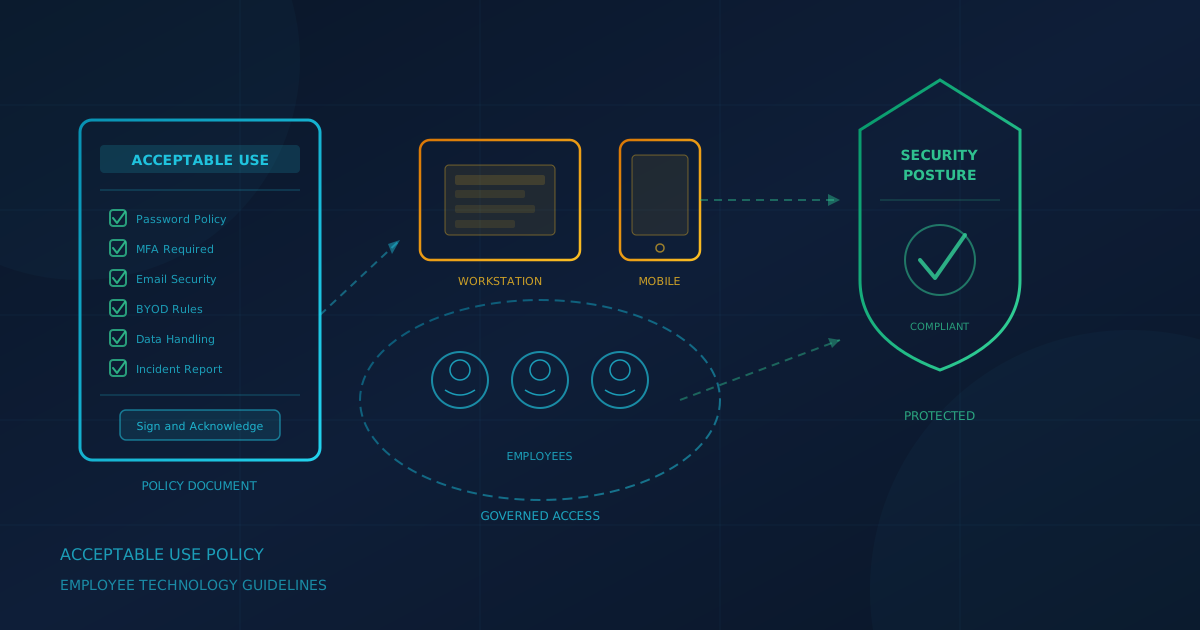
Acceptable Use Policy for Employees: A Guide
An acceptable use policy for employees tells staff how to use company technology safely. Here is what sections to include, based on CCCS and CISA guidance.
Read Article →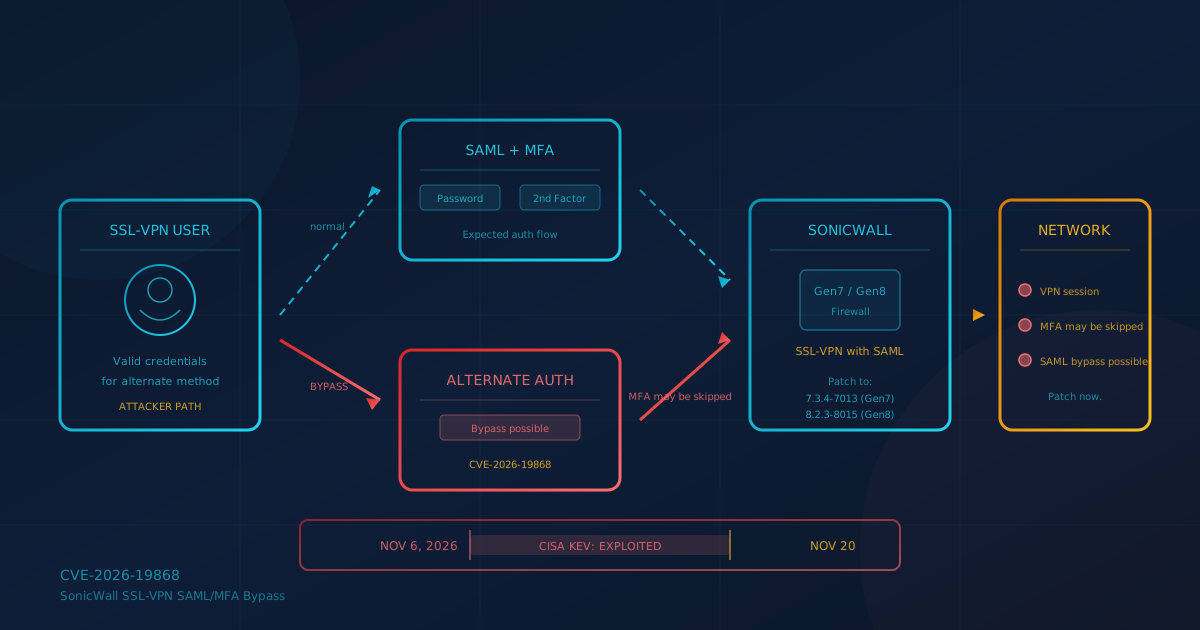
SonicWall MFA Bypass: Patch SSL-VPN Now
CVE-2026-19868 lets attackers bypass SAML and MFA on SonicWall SSL-VPN. CISA added it to KEV on November 6, 2026. Patch Gen7 and Gen8 firewalls now.
Read Article →